Powershell

Check Enterprise App SSO before changing email addresses with PowerShell
Alex Mags

new mail broken SSO

Changing everyone’s email address sounds like an Exchange mail job. Until someone asks which business applications use that address to identify people at sign-in.

You can open each Enterprise App in Entra portal to inspect its SSO configuration. Fine for five apps. Less appealing for a few hundred. This post walks through enumerating your Entra ID Enterprise apps with Microsoft Graph to find the apps, then using an undocumented Entra portal API to retrieve the SSO claims configuration and turn it into a CSV report.
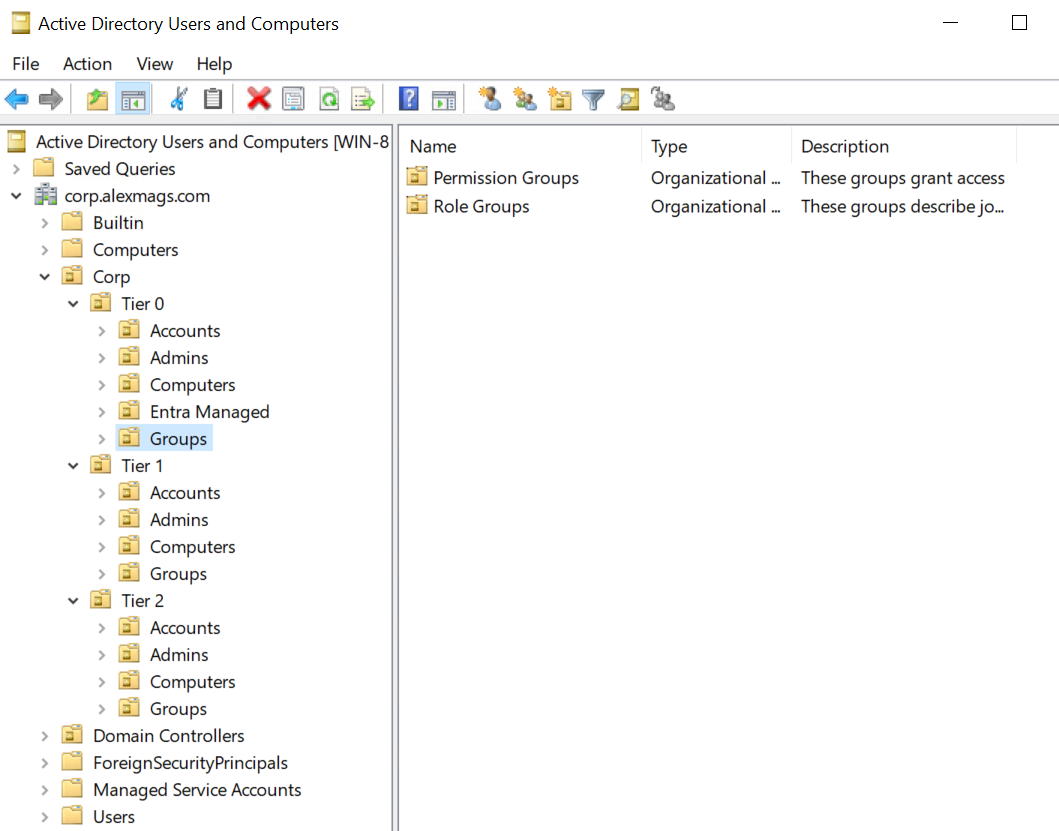
Active Directory Tiered Administration Model

Alex Mags

tiered admin model

The Active Directory Tiered Admin Model is a way to organise AD users and groups with very clear boundaries between standard user accounts and their permission groups, server and application administrative accounts and groups, and domain wide access accounts and groups. Creating and enforcing these boundaries hinders privilege escallation from desktop/user level access to domain compromise. Here’s some automation to set it up.

LDAPS with self-signed certificate

Alex Mags

Azure badger “Create a picture in the style of a pixar movie of a friendly badger, working in an office IT department, using encryption to secure Microsoft Active Directory” - bing chat

This post describes how to keep user passwords transmitted in LDAP authentication requests safe. Lightweight Directory Access Protocol (LDAP) is an open standard for directories. It underpins Microsoft Active Directory Domain Services (ADDS). Applications need to check in with a central directory to authenticate user sign-ins. Other authentication protocols oAuth,SAML,Kerberos, even NTLM are prefered but still, even today, you’ll need to accomodate self-hosted business applicaitons that only support LDAP for authenticaiton. In my experience these are often JAVA developed apps or apps hosted on Linux. This post has some PowerShell generate encryption certificates (private and public keys) to enable SSL encrypted LDAPS communication with domain controllers.

Auto Configure Git client proxy authentication

Alex Mags
This post has some PowerShell to make Git client work on Windows in corporate environment. Short version Use the Microsoft Credential Manager for Git. Don’t expose passwords in plaintext in Git config or environment variable. The Microsoft Credential Manager will store creds for proxy amd git repo in Windows Credential Manager Git client doesn’t accept domain name in Git config, when you enter creds in Credential Manager change ID to <userID> format Automatically configurge Git client to authenticate with corporate proxy Git client doesn’t support Web Proxy Auto Discovery (WPAD).

PowerShell wait music

Alex Mags
My long running PowerShell scripts now have background musak thanks to: http://www.adminarsenal.com/admin-arsenal-blog/powershell-music-remotely https://www.youtube.com/watch?v=FsoIfkNQYEg http://youtube-mp3.org/ $scriptDir = Split-Path -Path $MyInvocation.MyCommand.Definition -Parent $musakFilePath="$scriptDir\musak.mp3" $wmplayer = New-Object System.Windows.Media.MediaPlayer $wmplayer.Open($musakFilePath) Start-Sleep 2 # This allows the $wmplayer time to load the audio file $duration = $wmplayer.NaturalDuration.TimeSpan.TotalSeconds $wmplayer.Play() $stopwatch=[system.diagnostics.stopwatch]::StartNew() while ($stopwatch.Elapsed.Seconds -lt $duration) { Write-Progress -Activity "Doing stuff, please hold…" -status "$($stopwatch.Elapsed.Seconds) seconds" -percentComplete ($stopwatch.Elapsed.Seconds / $duration*100) # do something # break when done start-Sleep -s 1 } $wmplayer.

AD authentication to AWS from PowerShell

Alex Mags
I’ve done a couple of other posts on using AD credentials with AWS API. You setup AWS IAM to trust AD Federation Services (ADFS) for authentication. You get temporary access keys to use with the AWS API. This is safer than making lots of IAM accounts with long term passwords (Secret Access Keys) that end up embedded in code and stored who knows where. See previous posts for an overview of AD authentication to AWS.

AWS API without keys

Alex Mags
Hey there Enterprise Administrator! Avoid storing AWS API keys by using Windows authentication instead[/caption] Are you an Enterprise investigating AWS? Don’t want to become a security news story like these guys? https://www.google.co.uk/search?q=news+aws+secret+access+key+hack Are you used to multiple levels of physical and logical security for access to your equipment? https://www.youtube.com/watch?v=_qc5TG2ulx8 Is access to your VPC config shielded by nothing but some AWS API credentials? (which are probably stored in plain text..) Can your AWS credentials be used from the public internet (instead of only from the Office)?